Down Under and Out: How the Fall of TeamPCP Unmasked the Masterminds Behind the Longest-Running Software Supply Chain Attack
By Global Security Desk
Authorities in Australia, acting in a joint operation with the United States Federal Bureau of Investigation (FBI) and Western Australia Police, have arrested two men believed to be core operators of TeamPCP. The prolific cybercrime and data extortion collective is accused of orchestrating what security analysts have categorized as the longest-running and most disruptive software supply chain attack spree in the history of the digital ecosystem.
According to an official statement released by the Australian Federal Police (AFP), two men from Western Australia, aged 21 and 23, were taken into custody following an intensive cross-border investigation. The suspects are accused of being key architects in a "sophisticated cybercrime syndicate that allegedly created malicious open-source software to rob thousands of global businesses."
While the AFP initially withheld the identities of the defendants, Australian broadcaster ABC News later confirmed that the 21-year-old suspect is Ruben Ian Thomson of the affluent Perth suburb of Cottesloe, while the 23-year-old suspect has been identified as Michael Gaebler, widely known in threat intelligence circles by the hacker handle @pcpcasper. Both men were denied bail or held without a formal bail request during their initial appearance at the Perth Magistrates Court, facing a combined 14 cybercrime offenses.

The takedown marks a monumental milestone in the global fight against software supply chain manipulation. It follows months of relentless investigative work by private security researchers—most notably independent journalist Brian Krebs—who managed to unmask the real-world identities, aliases, and operational blunders of the syndicate’s leadership long before federal agents kicked down their doors.
Main Facts: The Anatomy of the TeamPCP Syndicate
TeamPCP first vaulted onto the international cybercrime scene in late 2025, rapidly cementing its reputation by embedding malicious code into hundreds of widely used open-source software tools. Rather than targeting enterprise firewalls directly, the group weaponized the modern software development pipeline, exploiting the inherent trust developers place in third-party code repositories.
At the heart of their campaign was Shai-Hulud, a self-propagating malicious worm. The malware targeted open-source programs maintained by developers whose credentials at public code repositories, such as GitHub or NPM, had been compromised via sophisticated phishing campaigns or credential-stuffing attacks.
Writing for Wired, journalist Andy Greenberg described TeamPCP’s core methodology as a cyclical exploitation loop:

"The hackers gain access to a network where an open-source tool commonly used by coders is being developed. The hackers plant malware in the tool that ends up on other software developers’ machines… The malware allows TeamPCP’s hackers to steal credentials that let them publish malicious versions of those software development tools, too. The cycle repeats, and TeamPCP’s collection of breached networks grows."
The group’s operational footprint extended far beyond traditional web applications. In March, TeamPCP executed a high-impact supply chain attack targeting artificial intelligence infrastructure by compromising LiteLLM, an open-source AI gateway connecting users to more than 100 different large language models (LLMs). According to an analysis by the security firm CloudSEK, the attack harvested cloud service keys and sensitive secrets from more than 2,500 organizations, including many of the world’s leading technology firms.
By May, TeamPCP claimed responsibility for compromising at least 3,800 code repositories at Microsoft-owned GitHub, an exploit triggered after a GitHub developer installed a browser extension compromised by the group’s malware.
Security analysts emphasize that TeamPCP was less of a traditional, hierarchical criminal crew and more of an organic amalgamation of threat actors drawn from multiple underground gangs. Austin Larsen, a principal threat analyst with the Google Threat Intelligence Group, noted:

"It is not a structured criminal crew with a single operator. It is a peer community of individually skilled actors, with one clear center of gravity."
That center of gravity was heavily interconnected with other notorious extortion brands through a Matrix chat server dubbed "Cybercats." The server functioned as a daily digital war room for figures like Boxturtle (linked to data breach brokers selling stolen files from automotive giants like BMW, Audi, Honda, Mercedes-Benz, Volvo, and Toyota) and SeesawSec (the operator behind Fulcrumsec, which claimed credit for ransomware and extortion campaigns against Novo Nordisk, LexisNexis, and Avnet).
Chronology: The Rise, Climax, and Collapse of Ellis and Company
The unraveling of TeamPCP’s leadership traces back to a trail of digital breadcrumbs and severe operational security (OPSEC) failures committed by its primary spokesperson and self-described leader, Ruben Thomson—who operated under aliases such as EllisD25, BulkDMT, Express, and Deadcatx3.
2018–2022: The Underground Genesis
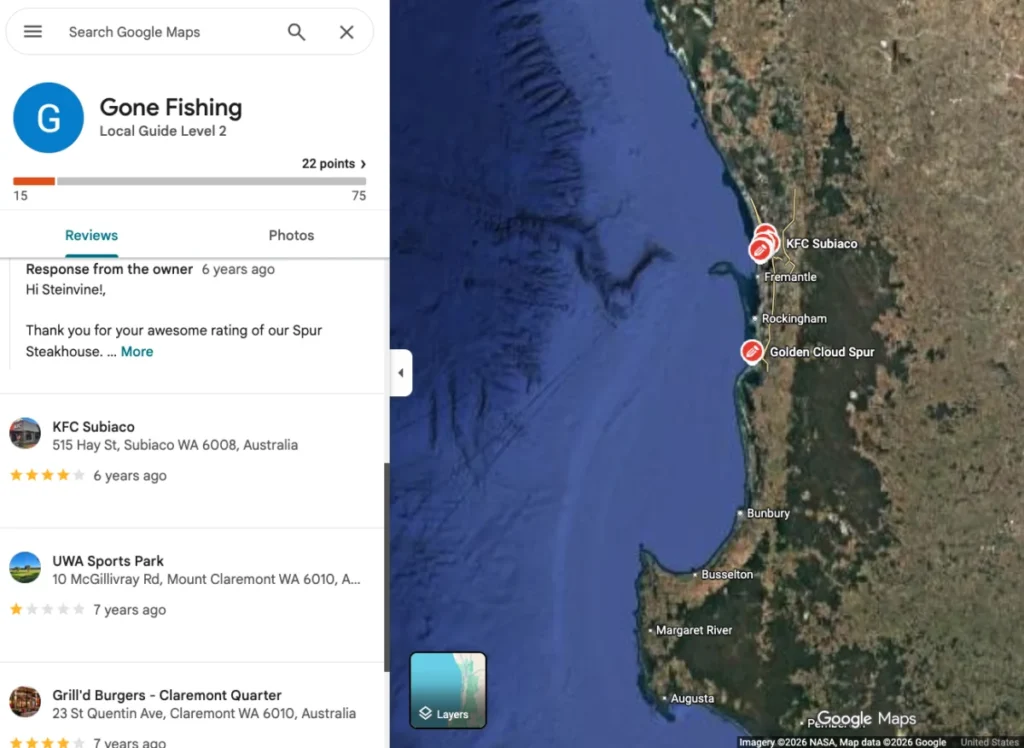
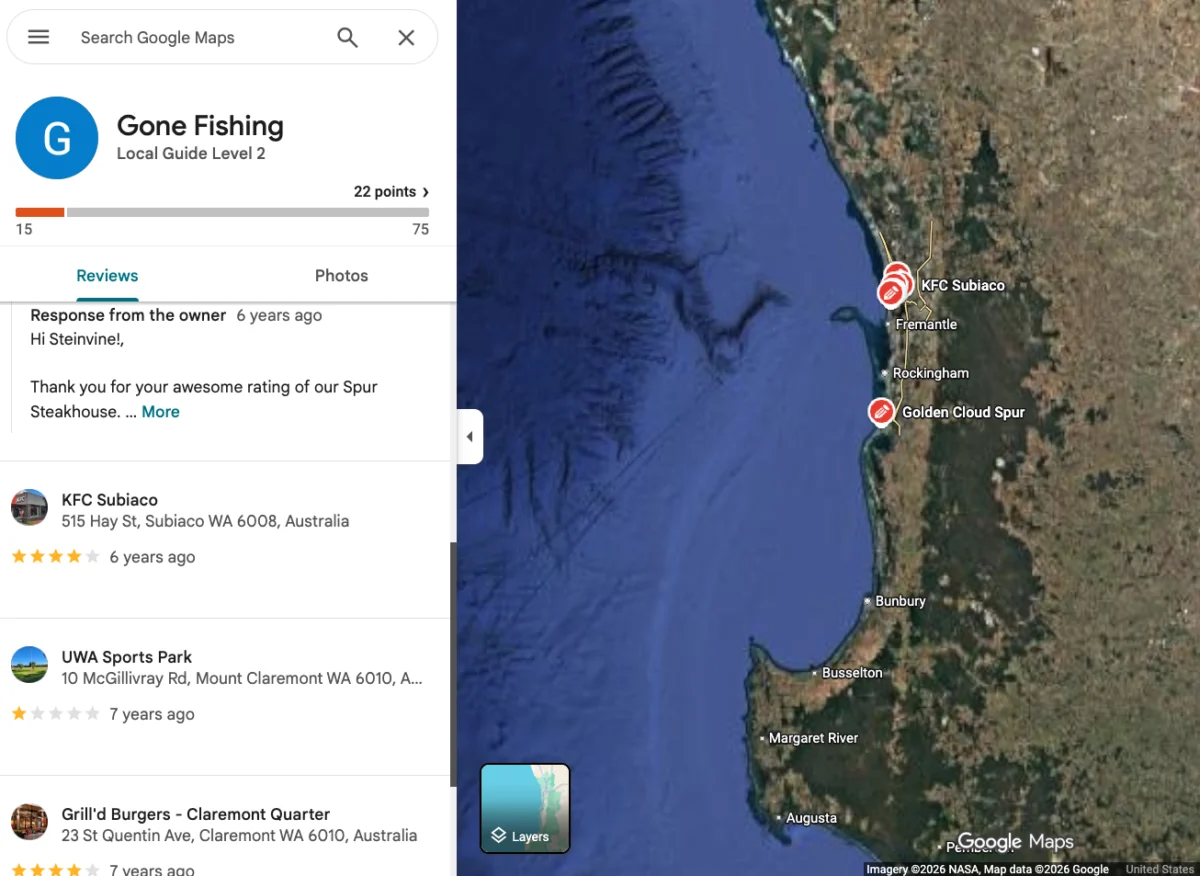
Long before TeamPCP was a household name among Chief Information Security Officers (CISOs), Ruben Thomson maintained a quiet but persistent footprint on English-language cybercrime forums like Altenen, Nulled, and Raidforums. Using email addresses tied to family domains in Perth—such as [email protected] and [email protected]—Thomson dabbled in proxy vending, digital storefronts selling discounted electronics via domains like rubenthomson.com, and scamming forum members under the handle XmasSnow by peddling fake software exploits.

Late 2025: The Birth of Shai-Hulud and Global Exploitation
By late 2025, Thomson had converged with other malware developers to form TeamPCP. Utilizing South African residential IP addresses and virtual private servers, Thomson’s alter ego (Persy_PCP / BulkDMT) began orchestrating global supply chain injections. During this period, Thomson openly discussed personal struggles with methamphetamine and synthetic narcotics on forums, noting that while his family had financial stability, his substance abuse issues had detached him from traditional support structures.
To accelerate its operational reach, TeamPCP embraced cyclical recruitment. In May, the group released the source code for the third iteration of Shai-Hulud and launched a contest offering $1,000 in Monero (XMR) cryptocurrency to the participant who could compromise the highest number of software downloads. According to security firm Dataminr, the baseline cash prize was dismissed by the group as a "participation trophy," designed primarily to identify and acquire high-value malicious access harvested by external participants on a massive scale.
June–July 2026: Investigative Breakthrough and Signal Interviews
In June 2026, independent security researcher Brian Krebs mapped the digital infrastructure connecting the email address [email protected] (used by the forum alias Express) to Perth-based passive DNS records, QNAP network storage devices, family business registrations, and an Upwork freelance profile for Ruben Thomson.
In early July, Krebs conducted an extensive interview with Thomson (referred to as Ellis) via the encrypted messaging app Signal. Ellis was remarkably candid about his motivations:

"Blackhatting is fun. There are actual rewards and incentives to learn and you grow with your team. Without qualifications, no employer will even take the time to hear you out."
Ellis claimed he had stepped back from active cybercrime operations in March 2026, shortly before the LiteLLM supply chain attacks, stating he had earned a modest grand total of roughly $20,000 through his association with TeamPCP. Despite acknowledging his impending doom, Ellis displayed mixed emotions regarding his future, admitting that his struggles with synthetic drugs—ranging from ketamine and 2C-B to synthetic DMT—dominated his daily existence.
August 2026: The Raid
On the morning of Wednesday, August 26, 2026, the Australian Federal Police executed raids in Western Australia, arresting Ruben Thomson (21) and Michael Gaebler (23). The suspects were remanded into custody ahead of their next scheduled court appearance on September 18.
Supporting Data & Threat Intelligence Analysis
Security telemetry gathered by prominent threat intelligence firms illustrates the unprecedented scale of TeamPCP’s operations:

- CloudSEK Metrics: The LiteLLM campaign compromised cloud service tokens belonging to more than 2,500 distinct corporate entities, exposing internal developer secrets across Fortune 500 enterprises.
- Flashpoint and Intel 471 Insights: Historical logs revealed that TeamPCP operators routinely hopped between jurisdictions, utilizing VPN endpoints in South Africa while maintaining residential footprints in Western Australia.
- The HackerOne Blunder: In one of the most egregious OPSEC failures in modern cybercrime history, Ruben Thomson registered an account on the bug bounty platform HackerOne under the username
Deadcatx3—the exact handle previously flagged by threat analysts as a primary TeamPCP alias. - Corporate Registrations: Public business records from the Australian Business Register show Thomson registered several entities with ironic or careless nomenclature, including Secure Computing Solutions, Tensor Industries, and OPSEC Express (directly mirroring his forum alias Express).
Official Responses and Industry Implications
Law enforcement agencies praised the cross-border cooperation that led to the arrests. The AFP highlighted that the disruption of the syndicate marks a critical victory against automated supply chain threats.
Industry experts, however, point out that TeamPCP represents a dangerous evolutionary step in modern threat landscapes. Charlie Eriksen, a security researcher at Aikido Security, noted that TeamPCP did not conform to traditional adversary profiles:
"They are not a state actor, not quite organized cybercrime, and not purely ideological. Their motivations seem to mix money, disruption, attention, and ideology."
Eriksen observed that the proliferation of generative artificial intelligence and large language models has compressed the learning curve for amateur hackers. Threat actors can now orchestrate multi-ecosystem supply chain attacks without possessing the foundational software discipline or operational caution typically exhibited by professional syndicates.

"They can be noisy, they can make mistakes. They can leave evidence everywhere. They can take risks that a professional criminal group or intelligence service would consider completely unacceptable. But that does not necessarily make them less dangerous. In some ways, it can make them more dangerous."
Legacy: Forcing a Reckoning in Software Security
Despite the chaos they sowed, security analysts argue that TeamPCP’s aggressive campaign may ultimately yield positive structural changes for the global software ecosystem.
In direct response to the Shai-Hulud worm and widespread package poisoning, GitHub introduced a mandatory three-day cooldown period for Dependabot in late July 2026. This administrative delay grants package maintainers and automated security scanners crucial time to evaluate newly published package updates and quarantine malicious payloads before they propagate downstream into production environments. Similar cooldown mechanisms have since been adopted across Python and JavaScript packaging ecosystems.
In the words of Charlie Eriksen, TeamPCP’s greatest and most ironic legacy is that they achieved in a matter of months what the supply chain security community had been advocating for years:

"They managed to wake up Microsoft to the fact that they had become negligent in terms of security. By compromising GitHub and stealing their source code, they humiliated Microsoft into action, making them finally act on what we had been asking them to do and take seriously for a while now."
As Ruben Thomson and Michael Gaebler await their September court dates in Perth, the digital community is left to contemplate a new era of cybersecurity—one where the most dangerous adversaries are no longer well-funded nation-state APTs, but reckless, hyper-accelerated digital subcultures operating out of suburban bedrooms.