Australian Federal Police Arrest Key Operatives Behind "TeamPCP" and the Notorious Shai-Hulud Software Supply Chain Attacks
By Global Security Desk
Main Facts: The Downfall of a Software Supply Chain Syndicate
In a coordinated transnational operation involving the Australian Federal Police (AFP), the Federal Bureau of Investigation (FBI), and the Western Australia Police Force, authorities have apprehended two men suspected of operating TeamPCP, a prolific cybercrime and data extortion syndicate. The suspects, aged 21 and 23, were taken into custody during early-morning raids in Western Australia. They face a combined 14 cybercrime charges relating to the deployment of malicious open-source software, widespread corporate extortion, and attacks that compromised thousands of global businesses.
Subsequent reporting by Australian media outlet ABC News identified the 21-year-old suspect as Ruben Ian Thomson of Cottesloe, a beachside suburb of Perth, and the 23-year-old suspect as Michael Gaebler. Australian courts denied bail for Thomson during their initial appearance at the Perth Magistrates Court, while Gaebler’s counsel did not request bail. Both men remain in custody pending their next scheduled court appearance.

TeamPCP rose to prominence in late 2025 as one of the most destructive and longest-running software supply chain extortion rings in internet history. Rather than targeting individual endpoints with standard ransomware, the syndicate embedded malicious code directly into widely used open-source libraries and developer repositories. Their crowning technological achievement—a self-propagating worm dubbed Shai-Hulud—automated the compromise of developer credentials on major platforms like GitHub and NPM, trapping organizations in a recursive cycle of trust exploitation.
Security analysts emphasize that TeamPCP differs significantly from traditional ransomware gangs or state-sponsored Advanced Persistent Threat (APT) groups. They functioned less as a rigid corporate enterprise and more as a decentralized peer community of digitally skilled threat actors. Their operations combined financial extortion, ideological chaos, and reckless operational security (OPSEC), culminating in a trail of digital footprints that ultimately led law enforcement straight to their doorsteps in Western Australia.
Chronology of an Escalating Campaign
The trajectory of TeamPCP’s digital campaign showcases a rapid escalation in scale, technical sophistication, and audacity.

Late 2025: Inception and the Shai-Hulud Worm
TeamPCP burst onto the cybercrime landscape by weaponizing developer trust. By stealing credentials from maintainers via phishing and credential-stuffing attacks, the group injected malicious payloads into legitimate open-source packages. When developers downloaded these libraries into their local development environments, the Shai-Hulud worm executed silently, harvesting cloud service keys, API tokens, and internal repository credentials to infect downstream projects automatically.
March 2026: The LiteLLM Breach
The syndicate executed one of its most consequential operations by targeting LiteLLM, an open-source AI gateway used to connect applications to over 100 large language models (LLMs). According to an analysis by security firm CloudSEK, the compromised LiteLLM package harvested cloud service keys and administrative secrets from more than 2,500 organizations, impacting major technology firms worldwide.
May 2026: GitHub Compromise and Contest Incitement
TeamPCP claimed responsibility for breaching at least 3,800 code repositories hosted on Microsoft-owned GitHub after an employee inadvertently installed a malicious browser or code extension. Around the same time, the group released the source code for the third iteration of Shai-Hulud and launched a hacking contest on Telegram. Offering a base prize of $1,000 in Monero (XMR)—dismissed by the group as a "participation trophy"—TeamPCP incentivized external participants to deploy the worm against high-download-count repositories, acting as an open recruitment drive for malicious access brokers.

June to August 2026: Identity Unraveling and Arrests
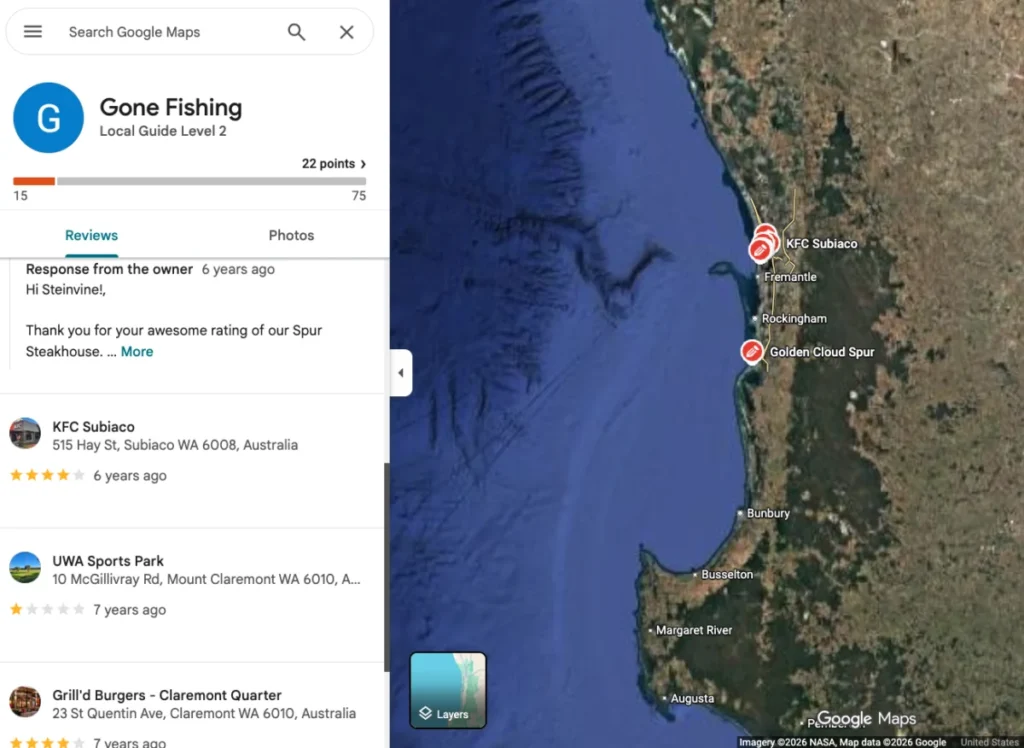
Security researchers, working alongside investigative journalists, tracked the digital breadcrumbs left by TeamPCP leaders across platforms like DarkForums, BreachForums, and a Matrix chat server dubbed "Cybercats." By mid-summer, investigators had correlated the online alias EllisD25/BulkDMT with Ruben Thomson. Following exclusive Signal interviews with journalists detailing his struggles with substance abuse and disillusionment, the AFP closed in. The simultaneous arrests of Thomson and Gaebler on August 27, 2026, effectively dismantled the core leadership team.
Supporting Data: The Digital Footprint and OPSEC Failures
The unmasking of TeamPCP offers a textbook case study in how brilliant technical execution can be completely undermined by poor operational security (OPSEC).
Cross-Forum Aliases and Infrastructure
Intelligence firms including Intel 471, Flashpoint, and SpyCloud mapped a constellation of handles operated by Ruben Thomson across underground English-language forums:

- DarkForums / Breachstars: Operating as
EllisD25,LSD, andBulkDMT, Thomson also peddled virtual private server (VPS) hosting under the moniker "DMT Host." - BreachForums: Utilizing the handle
Expressand registering accounts with the email address[email protected], Thomson advertised bulk access to stolen corporate assets, including 14 gigabytes of data extracted from South Africa’s State Information Technology Agency. - The "Cybercats" Matrix Server: Created by security researcher and exploit developer George Prepakis (
@kernelstub), the Matrix server served as a daily communication hub for members of multiple cybercrime factions, including data breach brokers like@xploitrsturtleandFulcrumsec.
Fatal OPSEC Missteps
Despite running syndicates capable of compromising thousands of enterprises, Thomson committed fundamental errors that linked his real-world persona to his cybercriminal alter egos:
- Corporate and Domain Registration: Thomson incorporated several Australian business entities—including Secure Computing Solutions, Tensor Industries, and ironically, OPSEC Express—using contact details and email addresses tied directly to his historical underground accounts.
- The HackerOne Blunder: In June 2025, Thomson registered an account on the vulnerability disclosure platform HackerOne using the username
Deadcatx3. Security firms had previously flaggedDeadcatx3as a primary alias utilized within TeamPCP operations. - Password and Email Reuse: Intelligence analysts discovered that Thomson routinely reused passwords like
joshuathomson1and tied his personal domain (thomson.org.au) to forum handles used for selling proxy services and discounted electronics as early as 2018.
Official Responses and Investigative Insights
Law enforcement agencies and threat intelligence leads have praised the cross-border cooperation that enabled the swift identification and capture of the suspects.
In its official media release, the Australian Federal Police characterized the suspects as the architects of a "sophisticated cybercrime syndicate that allegedly created malicious open-source software to rob thousands of global businesses." The joint operation underscored the growing necessity of international task forces in combating borderless code-injection threats.

Speaking anonymously to investigators and journalists before his arrest, Thomson (referred to as "Ellis" in interviews) expressed a fatalistic view of his cybercrime career. Having struggled with severe methamphetamine and psychedelic substance abuse while hopping between unstable living conditions, Ellis claimed he earned roughly $20,000 through his involvement with TeamPCP.
"Blackhatting is fun," Ellis remarked during an interview with security journalist Brian Krebs. "There are actual rewards and incentives to learn and you grow with your team. Without qualifications, no employer will even take the time to hear you out."
Austin Larsen, a principal threat analyst with the Google Threat Intelligence Group, contextualized the group’s structure:

"It is not a structured criminal crew with a single operator. It is a peer community of individually skilled actors, with one clear center of gravity."
Implications for the Software Supply Chain
Security experts agree that while the arrest of TeamPCP’s core leadership is a monumental win for law enforcement, the structural vulnerabilities exposed by the group will permanently alter how modern software is built, distributed, and maintained.
The Role of Generative AI and LLMs
Charlie Eriksen, a security researcher at Aikido Security, noted that TeamPCP represents an evolutionary leap in threat actor demographics.

"They are not a state actor, not quite organized cybercrime, and not purely ideological. Their motivations seem to mix money, disruption, attention, and ideology," Eriksen observed.
Eriksen highlighted that Large Language Models (LLMs) have drastically compressed the barrier to entry for complex cyberattacks. Threat actors can now bridge the knowledge gap between academic research papers and operationalizing devastating worms like Shai-Hulud without undergoing years of formal software engineering discipline. This has birthed a class of cybercriminals capable of immense collateral damage who are often too reckless to manage their own operational security.
The Rise of the "Cooldown" Era
Ironically, security experts have credited TeamPCP’s destructive campaign as the catalyst for long-overdue defensive upgrades across the global software ecosystem. Because the Shai-Hulud worm forced Microsoft and GitHub to confront systemic vulnerabilities in automated package updates, the industry has rapidly adopted defensive safeguards.

In late July, Microsoft introduced a mandatory three-day "cooldown" mechanism for Dependabot on GitHub. This buffer period delays the automated integration of newly published package versions, granting security automated scanners and maintainers vital time to catch and purge compromised code libraries before they propagate downstream. Similar cooldown frameworks have since been adopted across Python and JavaScript package ecosystems.
As Ruben Thomson and Michael Gaebler face the full weight of the Australian judicial system ahead of their September 18 court appearance, the legacy of TeamPCP remains clear: they woke the software industry up from a decade-long slumber, proving that the foundation of global digital infrastructure is only as secure as its most vulnerable maintainer.